MikroTik L009UiGS-2HaxD-IN Configuration
Learn how to configure MikroTik L009UiGS-2HaxD-IN for internet, WiFi 6, DHCP, NAT, VLAN, PPPoE, firewall, ISP and business networks in Kenya.
MikroTik L009UiGS-2HaxD-IN Configuration
How to Configure MikroTik L009UiGS-2HaxD-IN Step by Step
MikroTik L009UiGS-2HaxD-IN Configuration Guide | Kenya
The MikroTik L009UiGS-2HaxD-IN is a modern RouterOS v7 router designed for business networks, professional installations, ISPs, CCTV networks and advanced home users. It combines eight Gigabit Ethernet ports, a 2.5G-capable SFP interface, PoE, USB 3.0 and 2.4 GHz Wi-Fi 6 connectivity. MikroTik positions the L009 family as a major performance upgrade over the older RB2011 series.
If you are buying or setting up this router in Kenya, this guide explains how to configure the MikroTik L009UiGS-2HaxD-IN for internet access, LAN, Wi-Fi, DHCP, NAT, firewall, VLANs, PPPoE and ISP use.
You can view the MikroTik L009UiGS-2HaxD-IN on MikroTik Kenya or browse more MikroTik products in Kenya.
MikroTik L009UiGS-2HaxD-IN Overview
Before configuring the router, it helps to understand its hardware.
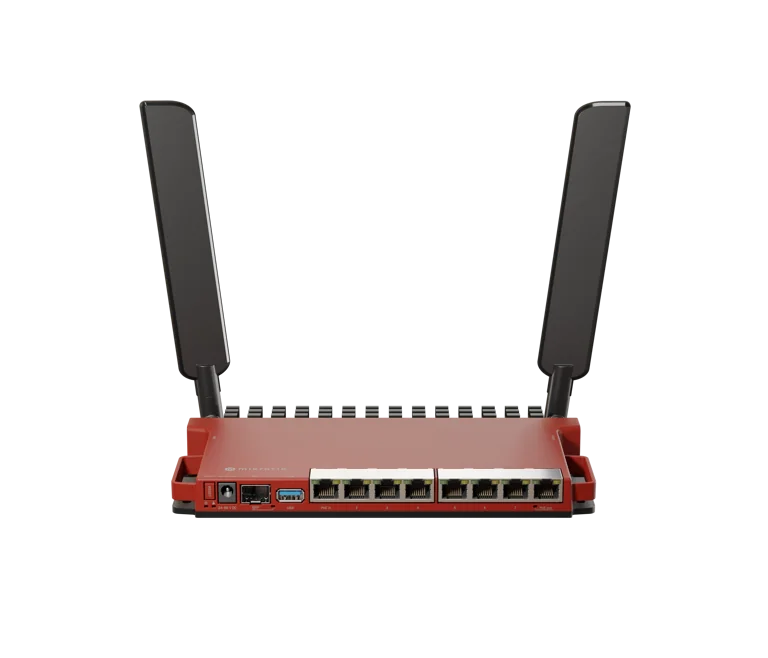
The L009UiGS-2HaxD-IN includes:
8 × Gigabit Ethernet ports
1 × SFP port with support for up to 2.5G
dual-core IPQ-5018 CPU
512 MB RAM
128 MB NAND storage
RouterOS v7
RouterOS Level 5 licence
2.4 GHz Wi-Fi 6
2 × external antennas
USB 3.0 Type-A
PoE input
Passive PoE output on Ether8
RJ45 serial console
The wireless interface supports 802.11b/g/n/ax, with a maximum advertised 2.4 GHz data rate of 574 Mbps.
Step 1: Connect to the MikroTik L009
Connect your laptop or desktop computer to one of the LAN Ethernet ports using an Ethernet cable.
You can configure the router using:
WinBox
WebFig
MikroTik mobile application
SSH
command-line terminal
For most users, WinBox is the easiest method.
Open WinBox and check the Neighbors tab. Your L009 should appear if the computer is connected directly to the router.
Select the router and log in.
If the router is brand new, follow the initial login instructions and create a secure administrator password.
Step 2: Change the Administrator Password
Do not leave a MikroTik router with weak or default credentials.
Create a strong password immediately.
For business and ISP deployments, it is also better to create individual administrator accounts for technicians rather than sharing one account.
This makes it easier to control access and troubleshoot unauthorized configuration changes.
Step 3: Update RouterOS
The L009 runs RouterOS v7. MikroTik ships the operating system preinstalled and licensed.
Before beginning a major configuration, check whether a stable RouterOS update is available.
Go to:
System → Packages
Then:
Check for Updates
Select the stable update channel unless you have a specific reason to use another release channel.
After updating RouterOS, also check whether the RouterBOARD firmware requires an upgrade.
Go to:
System → RouterBOARD
Upgrade if required, then reboot.
Step 4: Identify the WAN Interface
Decide which interface will connect to your upstream internet provider.
A common setup is:
Ether1 = WAN
The remaining Ethernet interfaces can then be used for the internal network.
You can rename interfaces to make future management easier.
For example:
ether1 → WAN
ether2 → OFFICE
ether3 → CCTV
ether4 → ACCESS-POINTS
ether5 → MANAGEMENT
Clear names become especially useful when configuring VLANs, firewall rules or multiple WAN connections.
Step 5: Configure the Internet Connection
How you configure WAN depends on your internet provider.
Common connection types in Kenya include:
DHCP
static IP
PPPoE
fibre ONT connection
Starlink
4G/5G modem
another upstream router
DHCP WAN Setup
If your ISP automatically provides network details, configure a DHCP client.
Go to:
IP → DHCP Client
Add a new DHCP client.
Select:
Interface: WAN
The router should receive an IP address, gateway and DNS details automatically.
Static IP Setup
If your ISP has provided a fixed IP address, enter the supplied details manually.
Go to:
IP → Addresses
Add the address to the WAN interface.
Then configure the gateway under:
IP → Routes
Also configure DNS under:
IP → DNS
PPPoE Client Setup
If your upstream provider gives you PPPoE credentials, go to:
PPP → Interfaces
Add:
PPPoE Client
Select your WAN interface and enter the supplied username and password.
Step 6: Create the LAN Bridge
For a typical business or home setup, combine the internal Ethernet ports into one bridge.
Go to:
Bridge
Create a bridge called:
LAN-BRIDGE
Then go to:
Bridge → Ports
Add your internal ports.
For example:
ether2
ether3
ether4
ether5
ether6
ether7
ether8
Do not add the WAN interface unless your specific topology requires it.
Step 7: Assign the LAN IP Address
Now assign a private IP address to the LAN bridge.
Go to:
IP → Addresses
Example:
192.168.10.1/24
Interface:
LAN-BRIDGE
This becomes the default gateway for devices on the local network.
Other private address ranges can also be used, such as:
192.168.20.1/24
or:
10.10.10.1/24
Choose a range that does not conflict with the upstream network.
Step 8: Configure DHCP Server
To allow computers, phones, access points and other devices to receive IP addresses automatically, configure DHCP.
Go to:
IP → DHCP Server
Select:
DHCP Setup
Choose:
LAN-BRIDGE
A simple example could be:
Network:
192.168.10.0/24
Gateway:
192.168.10.1
Address pool:
192.168.10.20-192.168.10.254
DNS:
Use your preferred DNS servers or the router itself.
Step 9: Configure DNS
Go to:
IP → DNS
Configure DNS servers as appropriate.
If clients should use the MikroTik as their DNS resolver, enable:
Allow Remote Requests
Make sure your firewall prevents external users on the WAN from abusing the router as an open DNS resolver.
Step 10: Configure NAT
For a standard private network using one upstream internet connection, configure source NAT.
Go to:
IP → Firewall → NAT
Create a new rule:
Chain:
srcnat
Out Interface:
WAN
Action:
masquerade
This allows devices on your LAN to access the internet through the WAN connection.
Step 11: Configure the Wi-Fi 6 Network
The L009UiGS-2HaxD-IN includes dual-chain 2.4 GHz Wi-Fi 6. MikroTik lists support for 802.11b/g/n/ax and up to 574 Mbps PHY rate on the 2.4 GHz radio.
Configure the wireless interface using the RouterOS WiFi menu.
Set:
SSID
country
security profile
password
frequency/channel
channel width
For example:
SSID:
Office-WiFi
Security:
WPA2/WPA3 where supported
Use a strong password.
For professional environments, do not put every device on the same wireless network if you can separate users using VLANs.
Step 12: Configure Wi-Fi Security
Avoid outdated or weak encryption.
Use modern security settings supported by your devices.
A business network may have separate wireless networks for:
Staff
Guests
Management
IoT devices
If you need multiple networks, configure appropriate VLANs and wireless datapaths rather than giving every device access to the same internal network.
Step 13: Configure the Firewall
A basic MikroTik firewall should protect the router itself and control unwanted traffic.
Typical logic includes:
accept established traffic
accept related traffic
drop invalid traffic
allow management from trusted LAN
allow required ICMP
block unsolicited WAN access
restrict WinBox and SSH
restrict management services
Do not blindly copy a firewall configuration from another network.
Firewall rules should match your actual network topology and management requirements.
Step 14: Restrict Router Management
Go to:
IP → Services
Disable services you do not need.
For example, if you do not use:
telnet
FTP
API
disable them.
For WinBox, SSH and WebFig, consider restricting access to your management subnet.
This is particularly important for public-facing ISP routers.
Step 15: Configure VLANs
One of the most useful features of the L009 is the ability to create segmented professional networks using RouterOS.
For example:
VLAN 10 – Administration
VLAN 20 – Staff
VLAN 30 – CCTV
VLAN 40 – Guest Wi-Fi
VLAN 50 – Management
Each VLAN can have its own:
subnet
DHCP server
firewall policy
bandwidth policy
For example:
Administration:
192.168.10.0/24
Staff:
192.168.20.0/24
CCTV:
192.168.30.0/24
Guest:
192.168.40.0/24
Use bridge VLAN filtering carefully. Incorrect configuration can disconnect the administrator from the router.
Step 16: Configure the SFP Port
The MikroTik L009 has an SFP interface that supports 1G and 2.5G connectivity with compatible modules.
This can be useful for:
fibre uplinks
connecting to managed switches
ISP infrastructure
office backbone connections
server-room networking
Install a compatible SFP module and check the interface status under:
Interfaces
Confirm that the link negotiates at the expected speed.
Step 17: Configure PoE
The router supports PoE input and Passive PoE output.
MikroTik specifies 802.3af/at PoE input and Passive PoE output on Ether8.
PoE output can be useful for powering compatible equipment such as:
access points
wireless CPEs
another supported MikroTik device
Before enabling PoE output, verify the voltage requirements of the connected device.
Passive PoE can damage equipment that is not designed for the supplied voltage.
Step 18: Configure Bandwidth Management
MikroTik RouterOS allows you to manage bandwidth using tools such as:
Simple Queues
Queue Tree
PCQ
PPP profiles
For example, a small ISP could create packages such as:
5 Mbps
10 Mbps
20 Mbps
50 Mbps
A business might instead prioritize:
VoIP
ERP systems
video conferencing
and limit less-important guest traffic.
Step 19: Configure PPPoE for ISP Use
The L009 can also be used in smaller MikroTik-based ISP deployments depending on subscriber count, bandwidth and workload.
For PPPoE:
Go to:
PPP → Profiles
Create profiles for your internet packages.
Then:
PPP → PPPoE Servers
Create the server.
Subscriber credentials can be managed under:
PPP → Secrets
For larger networks, RADIUS-based authentication is generally easier to manage than creating all customers manually on the router.
ISPs can also use Tajira for subscriber and billing workflows alongside MikroTik infrastructure.
Step 20: Configure Hotspot
The L009 can also be used in hotspot environments such as:
apartments
hotels
campuses
cafés
estates
small public Wi-Fi networks
Go to:
IP → Hotspot
Run the hotspot setup wizard.
Configure:
hotspot interface
address pool
network
DNS name
user profiles
If the hotspot is commercial, integrate the authentication and billing workflow carefully.
Step 21: Configure Multi-WAN Failover
The L009 has enough interfaces to support multiple internet connections.
For example:
WAN 1:
Fibre
WAN 2:
Starlink
You can configure the router so the second link takes over if the primary connection fails.
Common MikroTik approaches include:
route distance
recursive routes
Netwatch
scripts
Choose the simplest reliable method for your network.
Step 22: Configure Load Balancing
Where two active internet connections are available, RouterOS can also perform load balancing.
Possible approaches include:
PCC
ECMP
policy routing
Load balancing is more complex than failover.
Test carefully because banking applications, VPNs and other session-sensitive services may behave unpredictably if flows are distributed incorrectly.
Step 23: Configure the L009 for CCTV
For a CCTV network, create a separate VLAN or subnet.
Example:
CCTV VLAN:
192.168.30.0/24
Use firewall rules to limit which users can communicate with cameras and NVRs.
For remote access, use a secure VPN instead of exposing cameras directly to the internet whenever possible.
The L009 can therefore be useful for offices, warehouses, schools, hotels and apartment surveillance installations.
Step 24: Configure Remote Access
Technicians can manage the L009 remotely using secure methods such as:
WireGuard
IPsec
SSH
WinBox over VPN
Avoid exposing administrative services directly to the public internet unless access is strictly controlled.
VPN-based administration is generally preferable.
Step 25: Back Up the Configuration
After completing the setup, create both a binary backup and configuration export.
Go to:
Files → Backup
Also create a readable export from Terminal:
/export file=l009-config
Store these backups securely.
Make a new backup before major upgrades or configuration changes.
Recommended Configuration for a Small Business
A practical small-business L009 setup could be:
Ether1: WAN
Ether2–Ether7: LAN
Ether8: Access Point with PoE where compatible
SFP: Fibre uplink or managed-switch connection
Wi-Fi: Staff wireless network
VLANs:
Staff
Guest
CCTV
Management
WAN:
Primary fibre internet
Optional backup:
Starlink or LTE
This creates a flexible platform for office users, CCTV and wireless access.
Recommended Configuration for a Small ISP
For a small ISP, the L009 could be configured with:
WAN uplink
dedicated distribution interface
management VLAN
PPPoE server
customer address pool
firewall rules
bandwidth profiles
RADIUS integration where appropriate
For billing and subscriber operations, Tajira can complement the MikroTik environment.
However, as subscriber count and bandwidth grow, consider moving to more powerful hardware such as the MikroTik RB4011iGS+RM, RB5009 or CCR series.
L009UiGS-2HaxD-IN vs L009UiGS-RM
The MikroTik L009UiGS-RM is closely related to the L009UiGS-2HaxD-IN.
The major difference is wireless connectivity.
The L009UiGS-2HaxD-IN includes 2.4 GHz Wi-Fi 6, while the L009UiGS-RM is the wired-focused version. MikroTik says the wired version otherwise retains the same core platform features.
Choose the wireless version if you want built-in Wi-Fi.
Choose the RM version when Wi-Fi is not needed and you plan to use dedicated access points.
Where to Buy MikroTik L009UiGS-2HaxD-IN in Kenya
You can view the MikroTik L009UiGS-2HaxD-IN on MikroTik Kenya.
You can also browse MikroTik products in Kenya or compare MikroTik router prices in Kenya.
Additional MikroTik equipment is available through Orbitlink Solutions.
Frequently Asked Questions
How do I configure the MikroTik L009UiGS-2HaxD-IN?
Connect using WinBox or WebFig, configure the WAN connection, create the LAN bridge, assign an IP address, configure DHCP, NAT, firewall and Wi-Fi, then add services such as VLANs or PPPoE if required.
Does the L009UiGS-2HaxD-IN have Wi-Fi?
Yes. It provides dual-chain 2.4 GHz Wi-Fi 6 supporting 802.11b/g/n/ax.
How many Gigabit ports does the L009 have?
The L009UiGS-2HaxD-IN has eight Gigabit Ethernet ports.
Does MikroTik L009 support fibre?
Yes. It includes an SFP interface supporting 1G and compatible 2.5G connectivity.
Does L009 support PoE?
Yes. The router supports PoE input and Passive PoE output on Ether8.
Can I use the L009 for an ISP?
Yes, for appropriately sized deployments. The correct choice depends on subscriber count, bandwidth, firewall complexity and the number of queues or services running on the router.
Can I configure PPPoE on the L009?
Yes. RouterOS supports PPPoE server and client functionality.
Can I use the L009 for CCTV?
Yes. It can be configured with a dedicated CCTV subnet or VLAN and appropriate firewall and VPN policies.
Is the L009 better than RB2011?
MikroTik positions the L009 as the successor to the RB2011 and says it can be up to four times faster in many workloads while adding Gigabit ports, a modern ARM CPU, Wi-Fi 6 on this model and 2.5G-capable SFP connectivity.
Final Thoughts on MikroTik L009UiGS-2HaxD-IN Configuration
The MikroTik L009UiGS-2HaxD-IN is a flexible router for users who need Gigabit Ethernet, Wi-Fi 6, PoE, fibre connectivity and advanced RouterOS features in one compact device.
A basic setup requires WAN, LAN, DHCP, NAT, DNS, Wi-Fi and firewall configuration.
Professional installations can go further with:
VLANs
PPPoE
bandwidth management
hotspot
multi-WAN
failover
VPN
CCTV segmentation
fibre uplinks
For Kenyan businesses, technicians and smaller ISP environments, it offers a strong combination of features and expandability.
If you are planning to purchase the device, view the MikroTik L009UiGS-2HaxD-IN or visit MikroTik Kenya for other MikroTik routers and networking equipment.